Seeing a SAML “invalid signature” error when users try to log in through single sign-on is one of the most frustrating issues an IT administrator can face. The error message itself tells you almost nothing useful, users are locked out of their applications, and vendor documentation often skips the exact steps you need. I have spent countless hours debugging SAML signature failures across Okta, Entra ID, Keycloak, Google Workspace, and custom service provider implementations, and the good news is that the root cause almost always comes down to a small set of common problems.
In this guide, I will walk you through exactly how to fix SAML invalid signature errors in single sign-on, step by step. We will cover what the error means, why it happens, how to diagnose it with the right tools, and how to resolve it on every major identity provider platform. Whether you are a seasoned IAM engineer or a developer configuring SSO for the first time, you will find the specific fixes, debugging techniques, and prevention strategies you need to get your users back online quickly.
By the end of this article, you will know how to capture a SAML trace, extract and compare certificates, identify whether you are dealing with a certificate mismatch, an algorithm conflict, or an XML encoding issue, and apply the correct fix for your specific identity provider. Let us start with the most common cause and the fastest path to resolution.
Table of Contents
The Quick Answer: Most Common Cause and Fix
The most common cause of a SAML invalid signature error is an incorrect or expired identity provider (IdP) x509 certificate configured on the service provider (SP) side. The service provider receives a signed SAML response, attempts to verify the digital signature using the stored IdP certificate, and when the certificate does not match the one the IdP used to sign the response, verification fails.
To fix it, download the current signing certificate from your IdP’s metadata XML or admin console, update it in your service provider’s SAML configuration, ensure the signing algorithm (SHA256 vs SHA1) matches on both sides, and retest the login flow. In about 80 percent of cases, this single certificate update resolves the error immediately.
If updating the certificate does not fix it, the next most likely culprits are an expired certificate, a SHA1 vs SHA256 fingerprint algorithm mismatch, multiple certificates in the IdP metadata with incorrect ordering, or invalid XML characters from Active Directory attributes breaking the signature validation. We will cover each of these in detail throughout this guide.
What Is a SAML Invalid Signature Error?
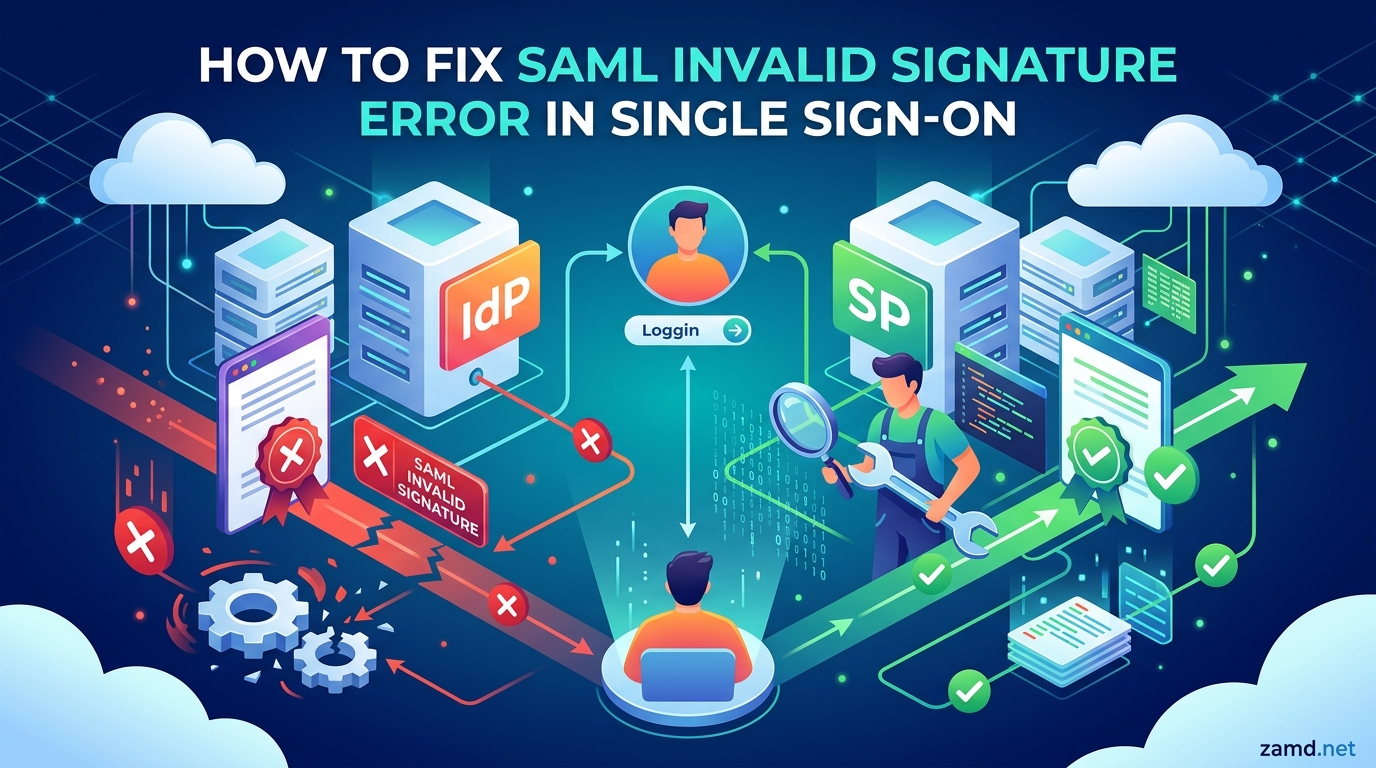
A SAML invalid signature error occurs when a service provider receives a SAML response from an identity provider but cannot cryptographically verify the digital signature attached to that response. The signature is what proves the response genuinely came from your trusted IdP and was not tampered with in transit. When verification fails, the SP rejects the entire response and blocks authentication.
This is a security mechanism, not a bug. Without signature verification, any attacker who could intercept network traffic could forge a SAML response claiming to be any user. The error is the SP doing its job by refusing to trust an unverified assertion.
The challenge is that the error message rarely tells you why verification failed. You might see messages like “Invalid signature on SAML Response,” “Signature verification failed,” “SAML message was signed by invalid signature,” or simply “SAML Assertion signature is invalid.” None of these pinpoint the actual root cause, which is why a systematic debugging approach is so important.
Here are the error message variations you are most likely to encounter across different platforms:
- “Invalid Signature on SAML Response” – Common in HashiCorp Terraform Enterprise and similar enterprise tools; usually a certificate mismatch.
- “Signature verification failed” – Common in Skilljar, Auth0, and general SAML libraries; indicates the stored certificate does not match the signing certificate.
- “SAML Message was signed by invalid Signature” – Common in Dynatrace and BMC Remedy; often points to an expired or rotated certificate.
- “SAML Assertion signature is invalid” – Common in Auth0 community discussions; can indicate algorithm mismatch or certificate formatting issues.
- “Failed to process SAML message, cause: invalid Signature” – Common in BMC Remedy SSO; frequently tied to expired IdP signing certificates.
How SAML Signature Verification Works
Understanding the verification process helps you debug faster because you can pinpoint exactly which step is failing. SAML signature verification follows a specific chain of cryptographic checks, and the error occurs at whichever step encounters a mismatch.
Here is how the process works step by step. When a user attempts to log in, the IdP generates a SAML response containing the user’s identity information as an XML document. The IdP signs this XML using its private key and embeds the corresponding public x509 certificate inside the SAML response in a dsig:X509Certificate element. The response is then sent to the service provider’s Assertion Consumer Service URL.
The service provider receives the response and performs the following checks in sequence:
- Certificate extraction – The SP extracts the
dsig:X509Certificatefrom the SAML response XML. - Fingerprint comparison – The SP computes a fingerprint (typically SHA1 or SHA256) of the extracted certificate and compares it against the stored IdP certificate fingerprint in its configuration.
- Signature validation – The SP uses the certificate’s public key to cryptographically verify the XML digital signature on the SAML assertion or response.
- Audience and Entity ID check – The SP verifies the response is intended for this specific application by checking the Audience and Entity ID values.
- Timestamp validation – The SP checks the
NotBeforeandNotOnOrAfterconditions to ensure the response is still valid and within the acceptable time window.
The invalid signature error specifically occurs at step 2 or step 3. If the fingerprint does not match, it means the certificate the IdP used to sign the response differs from what the SP expects. If the cryptographic signature validation fails even with a matching certificate, the XML may have been altered, the signing algorithm may differ, or the XML canonicalization may be producing different results on each side.
Understanding this flow is important because many administrators jump straight to certificate replacement without checking the algorithm setting or the Entity ID configuration. Those additional checks often reveal the actual root cause when the certificate itself is correct.
What Causes SAML Invalid Signature Errors?
After analyzing dozens of forum threads, StackOverflow questions, and vendor support articles, I have identified the root causes ranked by how frequently they occur in real-world SAML implementations. Going through these in order will help you identify your specific issue faster.
1. Incorrect or Outdated IdP Certificate (Most Common)
This is by far the most frequent cause, responsible for the majority of SAML signature errors. The IdP has rotated its signing certificate, but the SP still has the old certificate stored in its configuration. When the SP tries to verify the signature using the outdated certificate, verification fails because the key pair no longer matches.
This often happens silently. Your IdP may have an automated certificate rotation policy, or an administrator may have regenerated certificates during maintenance without coordinating with every service provider that relies on that IdP. Users suddenly cannot log in, and the only clue is the invalid signature error.
The fix is straightforward: download the new IdP signing certificate from your IdP admin console or metadata XML and update it in the SP configuration. We will walk through this in detail in the troubleshooting section.
2. Expired Signing Certificate
IdP signing certificates have expiration dates, and when they expire, some identity providers stop using them and switch to a new certificate automatically. If your SP still references the expired certificate, signature verification fails. The tricky part is that expiration may not trigger an obvious alert, so the first sign is usually users reporting SSO failures.
To check for this, look at your IdP’s SAML settings page where the signing certificate is displayed. Most admin consoles show the certificate’s validity period. If the certificate has expired, download the current active certificate and update your SP.
3. Multiple Certificates in IdP Metadata with Wrong Ordering
This is a surprisingly common issue that trips up even experienced administrators. Some identity providers, particularly Google Workspace, include multiple certificates in their metadata XML for rotation purposes. The XML signature library on the SP side (such as XMLSec) typically uses the first certificate in the metadata to attempt verification.
If the IdP is signing responses with a certificate that is not the first one listed, verification fails even though the correct certificate is present in the metadata. I have seen this exact issue reported in a StackOverflow thread with over 34,000 views, where a user discovered that working Google accounts had a different certificate order than broken ones in the same IdP metadata file.
The fix is to reorder the certificates in the IdP metadata so the currently active signing certificate appears first. Alternatively, extract just the active certificate and configure it directly in the SP rather than loading the full metadata XML.
4. SHA1 vs SHA256 Algorithm Mismatch
SAML certificates use a signing algorithm, and the IdP and SP must agree on which algorithm to use. If the IdP signs responses using SHA256 but the SP is configured to verify using SHA1 (or vice versa), signature verification fails even when the correct certificate is in place.
This issue commonly arises when one side defaults to SHA1 (older configurations) and the other defaults to SHA256 (modern security standards). A specific example from forum discussions: a user running ruby-saml found that openssl was calculating the fingerprint using SHA256, but ruby-saml defaulted to SHA1. Changing the fingerprint algorithm setting to SHA256 resolved the mismatch.
Check both your IdP signing settings and your SP verification settings to confirm they use the same algorithm. Most modern platforms default to SHA256, but legacy configurations may still use SHA1.
5. Entity ID or Audience URL Mismatch
While technically a different error class, Entity ID and Audience URL mismatches often surface alongside or instead of pure signature errors. The Entity ID is the unique identifier for the SP in the SAML federation, and the Audience URL must match exactly.
A common gotcha is a trailing slash. If your SP Entity ID is configured as https://app.example.com but the IdP sends https://app.example.com/ (with trailing slash), validation fails. Similarly, whitespace characters in the issuer URL can cause silent failures.
6. Invalid XML Characters from Active Directory Attributes
This is an insidious cause that is rarely documented but appears regularly in forum discussions. When Active Directory is the underlying directory for your IdP, certain AD attributes like objectSid contain binary data or characters that are not valid in XML. If these characters are included in the SAML response without proper encoding, they corrupt the XML structure and break signature validation.
The signature was computed over the original clean XML, but by the time the SP parses it, the invalid characters have altered the document. The cryptographic check then fails because the document hash no longer matches.
The fix is to filter out problematic AD attributes from the SAML claim mapping in your IdP, or ensure proper XML-safe encoding of all attribute values before they are included in the SAML response.
7. Certificate Formatting Issues
SAML libraries expect certificates in specific formats, and subtle formatting differences can cause verification to fail. For example, ruby-saml requires PEM certificate headers (-----BEGIN CERTIFICATE----- and -----END CERTIFICATE-----) to be included in the idp_cert setting. Forgetting these headers causes the library to fail silently on certificate parsing.
Other formatting issues include extra whitespace, line break differences between operating systems (CRLF vs LF), and base64 encoding errors during manual certificate copy-paste.
Step-by-Step Troubleshooting Guide
Now let us walk through the exact diagnostic process I use when troubleshooting SAML signature errors. Following these steps in order will help you identify the root cause quickly without skipping critical checks.
Step 1: Capture the SAML Response Trace
Before you can diagnose anything, you need to see the actual SAML response being sent between the IdP and SP. The easiest way to do this is using a browser extension called SAML Tracer (available for Firefox) or the browser DevTools network tab in Chrome or Edge.
If you are using the SAML Tracer extension:
- Install SAML Tracer from the Firefox add-ons repository.
- Open the extension and enable tracing.
- Navigate to your application and attempt to log in via SSO.
- When the login fails, switch to the SAML Tracer tab.
- Look for the SAML POST request to your Assertion Consumer Service URL.
- Click on the request and switch to the “SAML” tab to see the decoded XML.
If you are using Chrome DevTools:
- Open DevTools (F12) and switch to the Network tab.
- Attempt the SSO login.
- Look for the POST request to your ACS URL.
- Right-click the request and select “Save as HAR with content.”
- Open the HAR file and locate the SAMLResponse parameter in the form data.
- Base64-decode the SAMLResponse value to see the raw XML.
Save this decoded XML for the next steps. You will need it to extract the certificate and validate the signature.
Step 2: Extract the Signing Certificate from the SAML Response
Open the decoded SAML XML and look for the dsig:X509Certificate element. This is typically nested inside the dsig:KeyInfo element within the signature block. The value between the tags is the base64-encoded public certificate that the IdP used to sign this response.
Copy this certificate value. You will compare it against the certificate configured in your service provider.
Step 3: Compare Against Your SP’s Stored Certificate
Navigate to your service provider’s SAML configuration page and locate the IdP certificate setting. This might be stored as a certificate fingerprint, a full PEM certificate, or a metadata XML URL.
Compare the certificate from the SAML response against what is stored in your SP configuration. You can do this by:
- Fingerprint comparison – Compute the SHA256 fingerprint of the certificate from the SAML response and compare it to the fingerprint stored in your SP config.
- Direct comparison – If both certificates are in PEM format, compare them side by side.
- Online tool comparison – Paste both certificates into an online diff tool to spot differences.
If the certificates do not match, you have found your root cause. Update the SP configuration with the certificate from the SAML response.
Step 4: Verify the Signing Algorithm
If the certificates match but the error persists, check the signing algorithm. In the SAML response XML, look at the dsig:SignatureMethod element. It will specify the algorithm URI, such as http://www.w3.org/2001/04/xmldsig-more#rsa-sha256 for SHA256 or http://www.w3.org/2000/09/xmldsig#rsa-sha1 for SHA1.
Compare this to the algorithm configured in your SP. If there is a mismatch, update the SP to use the same algorithm the IdP is using.
Step 5: Validate the SAML Response Using an Online Tool
Online tools can help you validate the SAML response signature without needing to parse XML manually. The most commonly recommended tool is samltool.com, which allows you to paste a base64-encoded SAML response and see detailed validation results including signature status, certificate details, and decoded XML.
To use samltool.com:
- Copy the base64-encoded SAMLResponse from your trace.
- Go to samltool.com and select “SAML Response” validation.
- Paste the response and provide the IdP certificate when prompted.
- Review the validation results for signature status and error details.
Important security note: never paste production SAML responses that contain real user data into public online tools. Use a test account or redact sensitive attribute values before uploading.
Step 6: Check Entity ID and Audience URL
If the signature itself is valid but the login still fails, check for Entity ID and Audience mismatches. In the SAML response XML, locate the Audience element and compare it to your SP’s Entity ID. Also check the Issuer element in the SAML response to confirm it matches the IdP Entity ID in your SP configuration.
Watch for trailing slashes, http vs https protocol differences, and leading/trailing whitespace in these values.
Step 7: Check Certificate Expiration
Decode the IdP certificate and check its validity dates. If the certificate has expired, the IdP may have switched to a new certificate while your SP still references the old one. Download the current active certificate from the IdP admin console and update your SP.
Step 8: Retest the Login Flow
After applying fixes, clear your browser cache and cookies for the application, then attempt the SSO login again. Use SAML Tracer to confirm the response is now being accepted and check the SP logs for any remaining errors.
If the error persists, repeat the process starting from Step 1 with the new trace to see if the error details have changed. Sometimes fixing one issue reveals a secondary problem that was masked by the first error.
How to Verify and Fix Your IdP Certificate Configuration
The certificate verification and replacement process differs slightly depending on your identity provider, but the general approach is consistent. Here is how to obtain the correct certificate from common IdPs and update your service provider.
Downloading the IdP Signing Certificate
Most identity providers expose their signing certificate through a metadata XML URL. This URL is typically found in the IdP admin console under SAML settings or application integration details. When you visit this URL in a browser, you will see an XML document containing an md:IdPSSODescriptor element with one or more dsig:X509Certificate entries.
Some platforms also provide a direct download link for the certificate in PEM or DER format. If available, use this option as it reduces the risk of copy-paste errors.
Updating the SP Configuration
Once you have the correct certificate, update your service provider’s SAML configuration. The exact steps vary by platform, but generally involve:
- Logging into your SP application’s admin or configuration interface.
- Navigating to the SAML or SSO settings section.
- Locating the IdP certificate field (it may be labeled “IdP Signing Certificate,” “x509 Certificate,” or “Fingerprint”).
- Replacing the old certificate with the new one.
- Saving the configuration and testing the login.
If your SP accepts a metadata XML URL instead of a raw certificate, simply updating the URL or refreshing the metadata cache may be sufficient. Check your SP documentation for metadata refresh options.
Handling Certificate Fingerprints
Some service providers require a certificate fingerprint rather than the full certificate. A fingerprint is a hash of the certificate, typically computed using SHA1 or SHA256. To compute the fingerprint, use OpenSSL:
openssl x509 -in idp_cert.pem -fingerprint -sha256
This outputs the SHA256 fingerprint. If your SP requires SHA1, replace -sha256 with -sha1. Make sure to use the same algorithm the SP expects, or verification will fail even with the correct certificate.
Handling Multiple Certificates in Metadata
If your IdP metadata contains multiple certificates (common with Google Workspace during rotation periods), you need to determine which certificate is currently active. The IdP signs each response with one specific certificate, and that is the one you need.
To identify the active certificate, capture a SAML trace as described in the troubleshooting section and extract the dsig:X509Certificate from the response. This is your active signing certificate. Configure your SP with this specific certificate rather than loading the full metadata XML with all certificates.
SAML Debugging Tools and Techniques
Having the right tools makes SAML debugging dramatically faster. Here is a comparison of the most useful tools for different situations and skill levels.
SAML Tracer Browser Extension (Firefox)
SAML Tracer is a Firefox add-on that intercepts and decodes SAML messages in real time. It shows you the full SAML request and response XML, highlights the certificate and signature elements, and lets you export traces for sharing with colleagues or vendor support. This is the tool I reach for first when debugging SSO issues.
Best for: Quick initial diagnosis, visual inspection of SAML flows, and capturing traces to share with support teams.
Browser DevTools (Chrome, Edge, Firefox)
Every modern browser includes developer tools with a Network tab that can capture all HTTP requests, including the SAML POST to your ACS URL. While less specialized than SAML Tracer, DevTools are always available and can export HAR files for offline analysis.
To capture a SAML response using DevTools, filter the network requests by your ACS URL, find the POST request, and look at the form data for the SAMLResponse parameter. Base64-decode this value to see the XML.
Best for: Environments where you cannot install browser extensions, and for capturing HAR files to share with vendor support.
samltool.com Online Validator
samltool.com is a free web-based tool that validates SAML responses, decodes XML, verifies signatures, and provides detailed diagnostic information. You paste a base64-encoded SAML response and the tool shows you everything: the decoded XML, the certificate details, the signature status, and any validation errors.
Best for: Quick validation without installing tools, and for verifying signature status with a known-good certificate. Remember to redact sensitive user data before pasting production responses.
xmlvalidation.com
For XML structure issues specifically, xmlvalidation.com checks whether your SAML XML is well-formed and identifies any encoding or character problems. This is particularly useful when you suspect invalid XML characters from Active Directory attributes are corrupting the response.
Best for: XML parsing and encoding issues that are breaking signature validation at the document level.
OpenSSL Command Line
OpenSSL is invaluable for certificate-level debugging. Use it to inspect certificate details, compute fingerprints, verify certificate chains, and check expiration dates. The commands openssl x509 -in cert.pem -text -noout (inspect certificate details) and openssl x509 -fingerprint -sha256 (compute fingerprint) are the ones I use most frequently during SAML debugging sessions.
Best for: Certificate inspection, fingerprint computation, and verifying certificate validity dates.
Platform-Specific SAML Signature Fixes
Different identity providers have different configuration interfaces, default settings, and common gotchas. Here is platform-specific guidance for the most common IdPs.
Keycloak: Fixing “Invalid Signature in Response from Identity Provider”
Keycloak is a popular open-source IdP, and “Invalid signature in response from identity provider Keycloak” is a top related search. The most common Keycloak-specific issue involves the IdP certificate configuration in the Keycloak admin console.
To fix Keycloak SAML signature errors:
- Log into the Keycloak admin console.
- Navigate to your realm, then to Identity Providers.
- Select your configured SAML identity provider.
- Scroll to the “Identity Provider Settings” section.
- Verify the “Validate Signature” option is enabled.
- Check the “Signing Certificate” field contains the correct IdP certificate in PEM format.
- Make sure there are no extra line breaks or whitespace in the certificate.
- Verify the “Use Metadata Descriptor URL” is pointing to the correct IdP metadata endpoint if applicable.
- Save the configuration and retest.
A Keycloak-specific gotcha: if you import IdP metadata via URL, Keycloak caches the metadata. If the IdP rotates its certificate, Keycloak may still be using the cached old certificate. To fix this, go to the Identity Provider settings and click “Reload” on the metadata import, or manually update the certificate.
Okta: Fixing SAML Signature Errors
In Okta, the signing certificate is found under each SAML application’s settings. To obtain the correct certificate:
- Log into Okta admin console.
- Navigate to Applications and select your SAML application.
- Go to the “Sign On” tab.
- Click “View Setup Instructions.”
- Download the IdP certificate or copy the metadata URL.
Okta rotates signing certificates periodically. When this happens, you receive an email notification, but if the notification is missed or the update is not coordinated, SSO breaks. Always update your SP certificate when Okta notifies you of a rotation.
Entra ID (Azure AD): Fixing SAML Signature Errors
Microsoft Entra ID (formerly Azure Active Directory) provides the signing certificate in the enterprise application’s SAML configuration. To access it:
- Log into the Entra ID admin center.
- Navigate to Enterprise Applications and select your application.
- Go to “Single sign-on” settings.
- Download the certificate (Base64 or Raw) from the SAML Signing Certificate section.
- Note the expiration date shown next to the certificate.
Entra ID sends automated emails 60, 30, and 7 days before certificate expiration. Set up monitoring for these emails, or better yet, enable automatic certificate rollover in the SAML settings. Also verify that the “App Federation Metadata Url” is configured in your SP so it can automatically retrieve updated certificates.
Google Workspace: Fixing SAML Signature Errors
Google Workspace SAML signature issues most commonly involve the multiple certificate problem mentioned earlier. Google includes two certificates in its IdP metadata for rotation purposes, and some SPs incorrectly use the first (potentially inactive) certificate.
To fix Google Workspace SAML signature errors:
- Log into the Google Workspace Admin console.
- Navigate to Security > Authentication > SSO with SAML.
- Download the IdP metadata XML.
- Open the XML and identify which certificate is currently active.
- Capture a SAML trace to confirm which certificate Google is using to sign responses.
- Configure your SP with that specific certificate, not the full metadata XML.
If you must use the full metadata XML, try reordering the certificates so the active one appears first. This works with XMLSec-based libraries that use the first certificate in the list.
Advanced Causes: XML Encoding, Clock Skew, and Algorithm Mismatches
When the standard fixes do not resolve the issue, these advanced causes are worth investigating. They are less common but account for a significant portion of the remaining unsolved cases.
Invalid XML Characters from Active Directory
As mentioned in the causes section, Active Directory attributes can contain characters that are invalid in XML. The objectSid attribute is a common offender because it contains binary security identifier data. When this data is included in a SAML assertion without proper encoding, it corrupts the XML and breaks the signature.
To fix this, review the claim mapping rules in your IdP and either remove problematic AD attributes from the SAML response or ensure they are properly XML-encoded. In Entra ID, this means checking the user attribute mappings. In AD FS, review the claim rules in the relying party trust.
A developer on StackOverflow traced a weeks-long SAML signature issue to exactly this problem. The fix was filtering out the objectSid attribute from the SAML response, after which signatures validated correctly.
Clock Skew and Timestamp Validation
While not strictly a signature error, timestamp validation failures can produce error messages that look similar to signature errors. SAML responses include NotBefore and NotOnOrAfter timestamps, and if the system clocks on the IdP and SP differ by more than the allowed clock skew (typically 5 minutes), the response is rejected.
If you are seeing intermittent failures that only affect some users or sessions, check the system time on both the IdP and SP servers. Even a few minutes of drift can cause failures. Ensure both servers are synchronized using NTP.
Some SPs allow you to configure a larger clock skew tolerance. While increasing it can mask the problem temporarily, the correct fix is to ensure proper time synchronization across all servers.
XML Canonicalization Differences
XML digital signatures rely on canonicalization (c14n) to produce a consistent byte representation of the XML before computing the hash. Different canonicalization algorithms or implementations can produce different byte outputs, causing signature verification to fail even when the certificate and algorithm are correct.
This is rare but can occur when the IdP and SP use different XML security libraries. If you suspect this, check that both sides are using the same canonicalization method (typically “Exclusive XML Canonicalization” per the SAML specification).
Disabling Signature Verification as a Temporary Workaround
Some SAML libraries and SPs allow you to disable signature verification entirely. For example, in passport-saml (Node.js), setting wantAuthnResponseSigned: false skips signature validation. A developer on GitHub reported that this resolved their OneLogin SSO signature error.
Important warning: disabling signature verification is acceptable only as a temporary debugging step in a controlled test environment. It should never be used in production because it removes the cryptographic protection that prevents forged authentication responses. Any attacker who can intercept traffic could then forge SAML responses and impersonate any user.
How to Prevent SAML Signature Errors
None of the top competitors cover prevention strategies, which is surprising because most SAML signature errors are entirely preventable with proper planning. Here are the best practices I recommend based on years of managing SSO deployments.
Implement Certificate Expiration Monitoring
The single most effective prevention measure is tracking certificate expiration dates and setting up alerts well in advance. Most IdPs send automated email notifications before certificates expire, but these emails are easily missed.
Set up a monitoring system that tracks all SAML certificate expiration dates and sends alerts to multiple recipients at 90, 60, 30, and 7 days before expiration. Some organizations use dedicated certificate management tools, but even a simple spreadsheet with calendar reminders is better than no tracking at all.
Use Metadata URLs Instead of Static Certificates
Whenever possible, configure your SP to pull IdP metadata from a URL rather than storing a static certificate. This allows the SP to automatically retrieve updated certificates when the IdP rotates them, eliminating the most common cause of signature errors.
Most modern SPs support metadata URLs. If yours does not, petition the vendor to add this feature or schedule regular manual metadata refreshes as part of your operational procedures.
Document Certificate Rotation Procedures
Create a runbook for certificate rotation that includes every service provider that depends on each IdP. When a certificate is rotated, the runbook ensures every SP is updated before the old certificate expires. Include the specific steps for each platform since the update process varies.
Test SSO After Any Configuration Change
Any change to IdP configuration, SP configuration, or network infrastructure should be followed by an SSO login test. This includes firewall rule changes, load balancer updates, DNS changes, and TLS certificate renewals. Catching SAML issues early prevents user-facing outages.
Maintain a Test Account for SAML Debugging
Keep a dedicated test account that you can use to generate SAML traces without exposing real user data. This makes it safe to use online validation tools and share traces with vendor support. Having a known-good test account also gives you a baseline for comparison when things break.
FAQs
How to fix invalid SAML response?
To fix an invalid SAML response, verify your IdP signing certificate matches the certificate configured in your service provider, check for certificate expiration, ensure the signing algorithm (SHA256 or SHA1) matches on both sides, and validate the response using samltool.com. In about 80 percent of cases, updating the IdP certificate in the SP configuration resolves the error.
How do I fix a single sign-on error?
To fix a single sign-on error caused by invalid SAML signatures, ensure the IdP certificate in your SP configuration is correct and not expired, verify the signing algorithm matches between IdP and SP, confirm the Entity ID and Audience URL are identical on both sides, and check for clock skew between servers. If the certificate was recently rotated, update it in all connected service providers.
How to troubleshoot SAML login issues?
Troubleshoot SAML login issues by following these steps: 1) Capture a SAML trace using the SAML Tracer browser extension or browser DevTools, 2) Extract the dsig:X509Certificate from the SAML response, 3) Compare its fingerprint against your SP configuration, 4) Validate the response using samltool.com, 5) Check that Entity ID and Audience URL match exactly, 6) Verify the certificate has not expired, 7) Confirm the signing algorithm matches.
What does invalid SAML SSO link mean?
An invalid SAML SSO link error means the service provider received a SAML response from the identity provider but could not verify its digital signature. This typically happens because the IdP certificate in the SP configuration is incorrect, expired, or does not match the certificate used to sign the response. The SP rejects the unverified response and blocks authentication as a security measure.
Conclusion
Fixing SAML invalid signature errors in single sign-on comes down to a methodical debugging process. Start by capturing a SAML trace, extract the certificate from the response, compare it against your SP configuration, and update if there is a mismatch. If the certificate is correct, check the signing algorithm, Entity ID, certificate ordering, and XML encoding.
The vast majority of these errors are caused by certificate mismatches after rotation or expiration, so implementing certificate monitoring and using metadata URLs instead of static certificates will prevent most issues before they affect users. Bookmark this troubleshooting guide so you can work through the steps quickly the next time an SSO signature error appears.