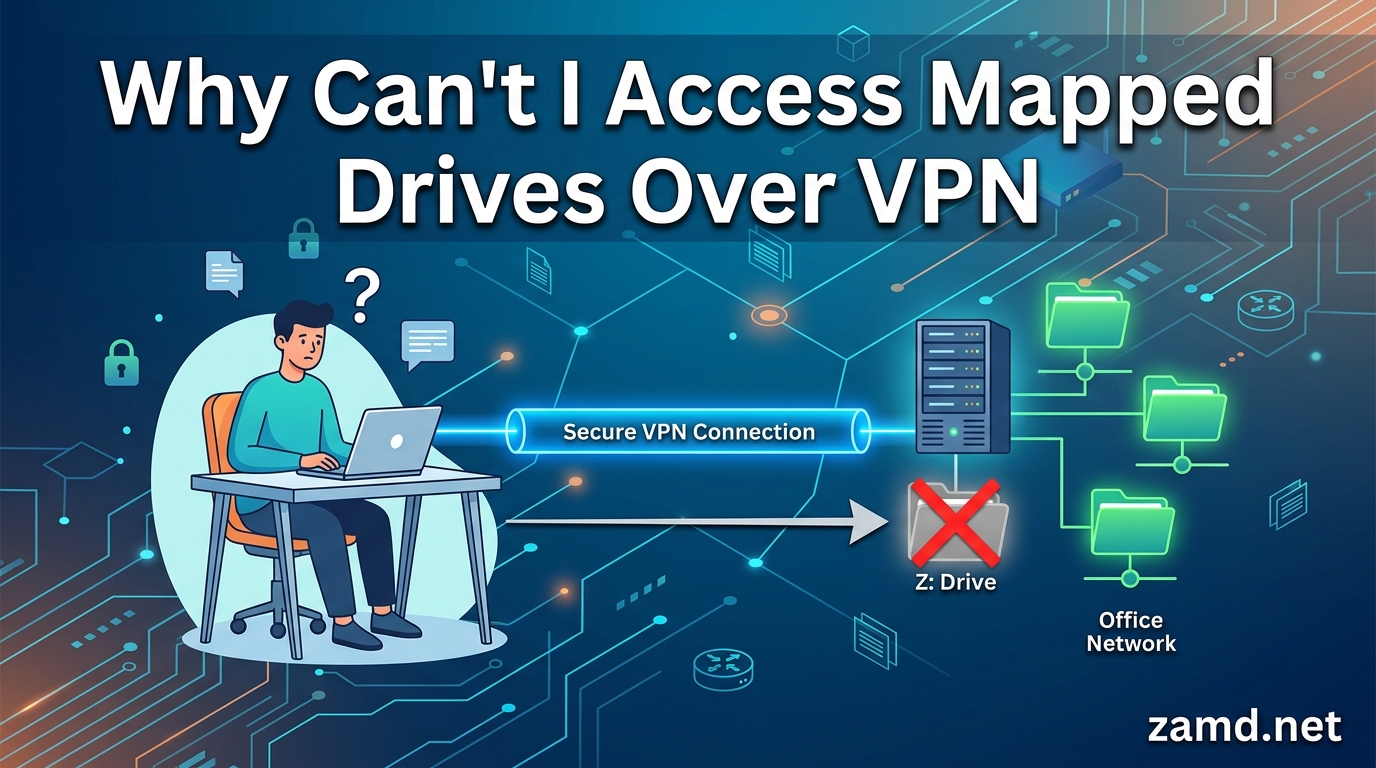
You sit down at your home desk, connect to the company VPN, and open File Explorer to grab a file from the shared drive. The drive letter is there, but it has a red X on it. Or worse, the drive is missing entirely.
If you are wondering why you can’t access a mapped network drive over a VPN, you are not alone. This is one of the most common frustrations for remote workers, and it happens because the VPN tunnel does not always properly route traffic, resolve server names, or authenticate your credentials the way the office network does.
Our team has spent years troubleshooting this exact problem across dozens of corporate environments. We have seen every variation: drives that work in the office but disappear at home, drives that map in a command prompt but not in File Explorer, and drives that suddenly stop working after a Windows update. In this guide, we will walk you through the six most common causes, a step-by-step diagnostic checklist you can run yourself, and specific fixes for each VPN client.
By the end, you will know exactly what is breaking your mapped drives and how to fix it. You can use this as a self-help guide before contacting your IT department, which saves everyone time.
Table of Contents
How VPN Connections and Mapped Network Drives Work Together
Before diving into fixes, it helps to understand what is actually happening under the hood. When things work, it feels invisible. When they break, knowing the mechanics helps you pinpoint the problem faster.
A mapped network drive is essentially a shortcut in Windows that assigns a drive letter (like Z:) to a shared folder on another computer or server. Windows uses the Server Message Block (SMB) protocol to talk to that shared folder and display its files as if they were on your local hard drive. The path Windows uses to find the shared folder is called a UNC path, and it looks something like \\fileserver\sharename.
A VPN creates an encrypted tunnel between your computer and your corporate network. All your network traffic (or some of it, depending on configuration) travels through that tunnel to reach servers, printers, and file shares on the office network. When everything is set up correctly, your mapped drive sends its SMB requests through the VPN tunnel, reaches the file server, and returns your files.
The problem is that many things can go wrong in that chain. The VPN might not be routing traffic to the file server’s subnet. Your computer might not be able to resolve the server’s name to an IP address because the internal DNS server is not being used. Your credentials might not pass through correctly. Or the VPN might connect after Windows has already tried and failed to map your drives at login.
Each of these failures produces a different symptom, and each requires a different fix. That is why a systematic approach works better than randomly trying solutions.
Six Most Common Causes of Mapped Drive Failures Over VPN
If you can’t access a mapped network drive over a VPN, one of these six root causes is almost always responsible. We have ranked them roughly by how often we see them in the field.
Root Cause 1: DNS Resolution Failures
This is the single most common reason mapped drives fail over VPN, and it is also the most underdiagnosed. Here is what happens: your office file server has a name like \\fileserver01. On the office network, Windows asks the internal DNS server “what IP address belongs to fileserver01?” and gets an answer instantly. Over VPN, your computer might still be using your home router’s DNS server or your ISP’s DNS server instead of the corporate DNS server. Those external DNS servers have no idea what “fileserver01” is, so name resolution fails silently and the drive never connects.
You can test this yourself. Open a command prompt and type nslookup fileserver01. If you get a timeout, a “server not found” error, or a response from your ISP’s DNS server, you have a DNS resolution problem. The fix is to make sure your VPN configuration pushes the internal DNS server address to your computer when it connects. If you do not control the VPN config, you can work around it by mapping the drive using the server’s IP address instead of its name: \\10.0.1.50\sharename instead of \\fileserver01\sharename.
On Reddit’s r/homelab, a user described this exact scenario: “This looks like a DNS problem. You can either configure your NAS with a FQDN and then add the domain to the VPN config or mount the shares with IP instead.” That is solid advice. The IP address workaround is the fastest fix when you cannot change DNS settings.
Root Cause 2: Split Tunneling Blocking File Server Traffic
Split tunneling is a VPN configuration that decides which traffic goes through the VPN tunnel and which goes directly to the internet. In a full tunnel setup, all your traffic goes through the VPN. In a split tunnel setup, only traffic destined for specific IP ranges (like the corporate subnet) goes through the VPN, while everything else goes directly out to the internet.
Think of it like a toll road. A full tunnel sends every car through the toll road. A split tunnel only sends cars heading to certain destinations through the toll road and lets the rest take local streets.
The problem arises when the split tunnel is not configured to include the subnet where your file server lives. Your VPN connects, you can reach the internet, but requests to the file server’s IP range are being sent out your regular home internet connection instead of through the VPN tunnel. They never reach the corporate network.
You can diagnose this by opening a command prompt and running route print. Look for the IP subnet of your file server in the routing table. If it is not listed as going through the VPN adapter, split tunneling is blocking it. The fix needs to be applied by whoever manages your VPN configuration, but you can confirm the problem yourself first.
Split tunneling also has another side effect. Some VPN clients with split tunneling intentionally block access to local network resources to prevent security risks. This means while you are connected to the VPN, you might lose access to your local printer or a home NAS. If your mapped drives point to local resources, split tunneling will cut them off.
Root Cause 3: Authentication and Login Timing Issues
Windows tries to reconnect mapped drives when you log in. But if your VPN connects after Windows login, the drives try to map before the VPN tunnel exists. They fail, and Windows gives up. You see a red X or a notification that says “Could not reconnect all network drives.”
This timing problem is especially common with corporate laptops that use Group Policy to assign mapped drives. Group Policy runs at login, applies the drive mappings, and Windows tries to connect immediately. If the VPN is not connected yet, every single mapped drive fails.
There are a few ways to fix this. First, connect to the VPN before logging into Windows. Many VPN clients support a pre-login or “start before logon” feature that establishes the VPN tunnel at the Windows login screen. This way, when Group Policy runs, the VPN tunnel is already active and the drives map successfully.
If pre-login VPN is not an option, connect to the VPN after logging in, then manually remap the drives or run gpupdate /force in a command prompt. This tells Windows to re-apply Group Policy, including drive mappings, now that the VPN is active. Some organizations also use a logon script or post-connect script that automatically remaps drives after the VPN connects.
Credential prompts are another authentication headache. If your mapped drive keeps asking for a username and password every time you connect, Windows is not remembering your credentials. You can fix this by opening Credential Manager (search for it in the Start menu), going to Windows Credentials, and manually adding the server’s address with your domain credentials. After that, Windows should stop prompting you.
Root Cause 4: Subnet Conflicts Between Home and Office Networks
This is a sneaky problem that trips up a lot of remote workers, and almost no troubleshooting guide covers it. If your home router uses the same IP subnet as your office network, your computer gets confused about where to send traffic.
Here is the scenario: your office network uses 192.168.1.x for its devices. Your home router, by default, also uses 192.168.1.x. When you connect to the VPN, your computer needs to send traffic for 192.168.1.50 (the file server) through the VPN tunnel. But your computer also thinks 192.168.1.x is your local home network. It sends the traffic to your home router instead of through the VPN, and the file server is unreachable.
To check for this, open a command prompt and run ipconfig /all. Look at your home Wi-Fi adapter’s IP address and your VPN adapter’s IP address. If your home adapter is on 192.168.1.x and your office file server is also on 192.168.1.x, you have a subnet conflict.
The fix is to change your home router’s DHCP range to something different, like 192.168.47.x or 10.0.0.x. Log into your home router’s admin panel, find the LAN or DHCP settings, and change the local IP address range. After rebooting your devices, the conflict disappears because your home network and office network now use completely different subnets.
We have seen this fix resolve “mysterious” drive mapping failures that stumped IT departments for weeks. The symptom is always the same: drives work fine for some remote workers but not others, and the difference is always the home router’s default subnet.
Root Cause 5: Group Policy (GPO) Delays and Failures
Many organizations use Group Policy Objects (GPO) to deploy mapped drives to users automatically. This is efficient for IT departments because they can assign drives based on Active Directory groups without touching individual computers. But GPO-based drive mapping introduces its own set of failure points over VPN.
The most common issue is timing. Group Policy processing happens at login and at periodic intervals afterward. If the VPN is not connected at login time, the GPO cannot map the drives because the file server is unreachable. Windows does not always retry failed drive mappings automatically.
Another issue is GPO processing speed over VPN. Group Policy involves querying the domain controller, processing policy settings, and applying preferences. Over a slow VPN connection, this process can time out or fail partway through. You might see some drives map successfully while others do not, which is a classic sign of GPO processing timing out.
To diagnose GPO issues, open a command prompt and run gpresult /r. This shows which Group Policy objects were applied and which failed. If you see your drive mapping policy listed under “Denied” or “Failed,” that confirms the problem.
The immediate fix is to connect to the VPN and then run gpupdate /force. This forces Group Policy to reprocess immediately. For a longer-term fix, ask your IT department to configure the GPO for “reconnect” behavior or to add the VPN’s DNS suffix to the policy’s targeting settings.
On Spiceworks, an IT professional described this exact problem: “I am having trouble with some mapped drives. They are mapped with GPO in place before I came along. I have a Windows 10 Pro workstation connecting to a Windows 2019 server via VPN.” The solution involved ensuring the VPN connected before login and running gpupdate after connecting.
Root Cause 6: Windows 11 and GlobalProtect TLS Issues
Windows 11 introduced stricter security defaults that have caused a wave of mapped drive failures, particularly for users of Palo Alto Networks’ GlobalProtect VPN. This is a newer problem that most troubleshooting guides do not address yet.
The issue involves TLS (Transport Layer Security) version restrictions. Windows 11 disables older TLS versions by default for security reasons. Some VPN configurations and file servers rely on TLS 1.0 or TLS 1.1, which Windows 11 blocks. When the VPN tunnel or the SMB connection tries to negotiate a security protocol that Windows 11 refuses to use, the connection silently fails or takes an unusually long time to establish.
On Microsoft’s Q&A platform, an administrator described the problem: “We deploy mapped drives via group policy. The drives map both inside the office and over the VPN when outside the office, however, when you are on the VPN outside the office not all drives are visible in File Explorer.” The accepted answer pointed to TLS and security group policies causing connection delays.
GlobalProtect users on Windows 11 have also reported a specific quirk: drives show up when mapped via the command line using net use but do not appear in File Explorer. This appears to be related to how GlobalProtect handles network adapter enumeration and split tunnel routing on Windows 11.
Fixes for this issue include updating GlobalProtect to the latest version, checking the split tunnel configuration in the GlobalProtect portal, and ensuring the file server supports TLS 1.2 or higher. Your IT department may need to update the server-side security settings. If you see this behavior, mention the Windows 11 TLS issue specifically to your IT team so they can investigate the right area.
Step-by-Step Diagnostic Checklist for Mapped Drive VPN Problems
Instead of guessing at solutions, run through this diagnostic checklist in order. Each step takes about 30 seconds and narrows down the problem quickly. Open a command prompt as administrator before you start.
Step 1: Verify VPN Connectivity
First, confirm your VPN is actually connected and passing traffic. Look at your VPN client to verify the connection status shows as connected. Then find the IP address of your file server (ask IT or check a working computer in the office) and try to ping it.
Run: ping 10.0.1.50 (replace with your file server’s IP address).
If the ping succeeds, your VPN is routing traffic to the corporate network. If it times out, your VPN is either not fully connected or split tunneling is blocking traffic to that subnet. Contact your IT department to verify the VPN routing configuration.
Step 2: Check DNS Resolution
Next, verify that your computer can resolve the file server’s name to an IP address. This is where most problems hide.
Run: nslookup fileserver01 (replace with your actual server name).
If you see the correct IP address, DNS is working. If you get a timeout, “server not found,” or a response from a public DNS server like 8.8.8.8, your VPN is not pushing the internal DNS server to your computer. The workaround is to map the drive using the IP address directly, and the permanent fix is to update the VPN DNS configuration.
Step 3: Inspect the Routing Table
Check whether traffic destined for the file server’s subnet is being sent through the VPN tunnel.
Run: route print
Look for the subnet that contains your file server’s IP address (for example, 10.0.1.0). Verify that the gateway for that route points to your VPN adapter, not your home router. If the route is missing or pointing to the wrong gateway, split tunneling is misconfigured.
Step 4: Test SMB Connection
Check whether your computer can reach the file share specifically, not just the server.
Run: net view \\10.0.1.50 (replace with your server’s IP).
This command lists the available shares on the server. If it works, your SMB connection is fine and the problem is likely with drive mapping or credentials. If you get “access denied,” you have an authentication problem. If you get “network path not found,” you have a routing or firewall problem.
Step 5: Check for Subnet Overlap
Verify that your home network and office network are not using the same IP range.
Run: ipconfig /all
Compare your home network adapter’s IP address with the file server’s IP address. If both start with 192.168.1.x (or any identical subnet), you have a conflict. Change your home router’s DHCP range to a different subnet to resolve this.
How to Map a Network Drive Over VPN (Step-by-Step)
If your drives are not mapping automatically, you can map them manually. This process works on both Windows 10 and Windows 11. Do this after your VPN is connected and you have verified connectivity.
Step 1: Open File Explorer and click on “This PC” in the left sidebar.
Step 2: Click the “Map network drive” button in the toolbar at the top. On Windows 11, click the three-dot menu (more options) and select “Map network drive.”
Step 3: Choose a drive letter from the dropdown. Pick one that is not already in use.
Step 4: In the Folder field, enter the network path. If DNS is working, use \\fileserver01\sharename. If DNS is not working, use the IP address: \\10.0.1.50\sharename.
Step 5: Check “Reconnect at sign-in” if you want the drive to map automatically every time you log in. Keep in mind this will only work if the VPN is connected at login time.
Step 6: Check “Connect using different credentials” if your VPN account and your file server account are different, or if you are on a non-domain-joined computer.
Step 7: Click Finish. Windows will attempt to connect. If prompted, enter your domain credentials in the format domain\username or [email protected].
If the mapping fails, check the error message. “The network path was not found” means a DNS or routing problem. “Access is denied” means an authentication problem. “The local device name is already in use” means the drive letter is taken.
You can also map drives from the command line, which gives you more detailed error messages. Run: net use Z: \\10.0.1.50\sharename /persistent:yes. Add /user:domain\username if you need to specify credentials. Command-line mapping is also useful when drives appear via net use but not in File Explorer, as mentioned in the Windows 11 section above.
VPN Client-Specific Fixes
Different VPN clients have different quirks that affect mapped drive behavior. Here are the specific fixes we have found for the most common enterprise VPN clients.
GlobalProtect (Palo Alto Networks)
GlobalProtect is widely used in enterprise environments, and it has specific issues with mapped drives on Windows 11. The most common problem is that split tunnel configuration routes traffic in a way that blocks file server access. Check with your IT team to verify that the split tunnel includes the subnet where your file server lives.
The second GlobalProtect issue is the TLS version conflict on Windows 11. Ensure you are running the latest version of GlobalProtect, as older versions have known compatibility issues with Windows 11’s stricter TLS defaults. If drives appear via net use but not in File Explorer, try restarting the Explorer process from Task Manager or rebooting after the VPN connects.
SonicWall NetExtender
SonicWall’s NetExtender client has known issues with persistent mapped drive connections. The drives often disconnect when the laptop wakes from sleep or when the VPN briefly drops and reconnects. The fix is to disable the “reconnect at sign-in” option for drives and instead use a post-connect script that remaps them automatically each time the VPN establishes.
SonicWall users also report DNS resolution problems similar to other clients. Make sure the NetExtender profile is configured to push the internal DNS server address to the client.
Sophos Connect
Sophos Connect users frequently encounter authentication failures with mapped drives, especially on non-domain-joined laptops. The solution is to store credentials in Windows Credential Manager before connecting. Add the file server’s IP address and UNC path with your domain credentials, and Sophos Connect will use them automatically.
Sophos also has a split tunnel configuration that can inadvertently exclude file server subnets. Verify the configuration includes all necessary corporate subnets.
OpenVPN
OpenVPN gives you the most control over DNS and routing configuration, which is both an advantage and a potential trap. If your OpenVPN configuration file does not include push "dhcp-option DNS 10.0.1.10" (with your internal DNS server’s IP), name resolution for internal servers will fail.
Check your OpenVPN configuration for the DNS push directive and the redirect-gateway setting. If split tunneling is configured, verify that the route to the file server subnet is included. OpenVPN’s log file, accessible from the client interface, provides detailed information about DNS and routing setup.
Advanced Fixes: PowerShell, Static DNS, and Always-On VPN
When the basic fixes are not enough, these advanced solutions can resolve persistent mapped drive problems. They are especially useful for IT administrators and power users who manage their own systems.
PowerShell Remap Script
One of the most effective solutions mentioned in IT forums but almost never published in a guide is a PowerShell script that automatically remaps drives after the VPN connects. The script reads the previous drive mappings from the Windows registry, waits for the VPN to establish connectivity, and then remaps each drive.
Here is a basic version of the script that you can adapt to your environment. Open PowerShell as administrator and create a script file:
$drives = Get-ChildItem -Path "HKCU:\Network" | ForEach-Object { Get-ItemProperty $_.PSPath }
foreach ($drive in $drives) { $letter = $drive.PSChildName; $path = $drive.RemotePath; net use ${letter}: $path /persistent:yes }
This script reads all previously mapped drive letters and UNC paths from the registry and remaps them. You can configure it to run automatically when the VPN connects by adding it as a post-connect action in your VPN client settings or by creating a scheduled task that triggers on the VPN connection event.
On Spiceworks, an IT professional shared that a similar post-connect script resolved their GPO drive mapping issues permanently. The script approach works because it bypasses the timing problem entirely: instead of relying on Group Policy to map drives at login, the script maps them after the VPN is confirmed active.
Static DNS Host Records
If DNS resolution is the problem but you cannot change the VPN DNS configuration, you can add a static host record to your computer’s hosts file. This tells Windows exactly which IP address belongs to the file server, bypassing DNS entirely.
Open Notepad as administrator, then open C:\Windows\System32\drivers\etc\hosts. Add a line like: 10.0.1.50 fileserver01. Save the file and run ipconfig /flushdns to clear the DNS cache. Now Windows will resolve fileserver01 to 10.0.1.50 without asking any DNS server.
This fix is reliable for individual computers but does not scale well for IT departments managing many machines. For enterprise environments, a better approach is to configure a static DNS record on the corporate DNS server or fix the VPN DNS push configuration.
Always-On VPN Configuration
For organizations that want to eliminate the login timing problem entirely, Windows Always-On VPN is the gold standard. Always-On VPN automatically connects before the user logs into Windows, ensuring that the VPN tunnel is active when Group Policy runs and mapped drives are applied.
Always-On VPN requires configuration on both the server side (Windows Server with Routing and Remote Access or a third-party VPN server) and the client side (deployed via Intune, Group Policy, or PowerShell). When configured correctly, it provides a seamless experience: the user logs in, and all mapped drives are already connected because the VPN was active before login.
This is the solution we recommend for IT departments that are tired of troubleshooting mapped drive issues for remote workers. The initial setup takes effort, but it eliminates the root cause for the majority of drive mapping failures.
Quick Reference: Symptoms and Their Most Likely Causes
Use this reference table to match your specific symptom to the most likely cause and the fastest fix. This is the decision tree that many forum users wish they had.
Drives work in office but not over VPN: This is almost always DNS resolution or split tunneling. Try mapping with the IP address to confirm.
Drives show a red X but reconnect when clicked: The VPN dropped and reconnected. Run a remap script or use gpupdate /force.
Drives do not appear at all after VPN connect: Check if Group Policy applied with gpresult /r. Run gpupdate /force after connecting.
Drives work via command line but not in File Explorer: This is a known Windows 11 + GlobalProtect issue. Restart Explorer or reboot after VPN connects.
Drives work for some users but not others: Check for subnet conflicts. Users whose home routers use the same subnet as the office will fail.
Drives prompt for credentials repeatedly: Store credentials in Credential Manager with the server’s UNC path and IP address.
Drives map slowly or time out: Check TLS version compatibility on Windows 11 and ensure the file server supports TLS 1.2 or higher.
Drives work with IP but not server name: DNS resolution failure. Add a hosts file entry or fix the VPN DNS configuration.
FAQ’s
How to access network drive through VPN?
To access a network drive through VPN, first connect to your VPN client and verify the tunnel is active. Then open File Explorer, click This PC, select Map Network Drive, choose a drive letter, and enter the UNC path of the shared folder (such as \\fileserver01\sharename). Check Connect using different credentials if prompted, and enter your domain username and password. If the server name does not resolve, try using the server IP address instead.
Can connect to VPN but cannot access network?
If your VPN is connected but you cannot access network resources, the most common causes are DNS resolution failures and split tunneling misconfiguration. Your VPN may not be pushing the internal DNS server to your computer, so server names do not resolve. Split tunneling may also be routing traffic to the file server subnet outside the VPN tunnel. Run nslookup to test DNS and route print to check routing.
How to bypass network blocking VPN?
If a network (such as a hotel or public Wi-Fi) is blocking your VPN, try switching VPN protocols (from IPSec to SSL/TLS), changing the VPN port number, or using a VPN with obfuscation support. However, if your question is about split tunneling blocking local network resources, the fix is to configure the VPN client to allow local LAN access or adjust the split tunnel routing to include the file server subnet.
Why are my mapped network drives not displaying?
Mapped network drives may not display in File Explorer due to several causes: the VPN connected after Windows login so Group Policy drive mappings failed, DNS cannot resolve the server name, split tunneling is blocking traffic to the file server, or on Windows 11 with GlobalProtect there is a known issue where drives appear via net use but not in File Explorer. Try running gpupdate /force after connecting to the VPN, or map the drive manually using the server IP address.
Do I need to connect VPN before or after logging into Windows?
You should connect to the VPN before logging into Windows if your mapped drives are assigned by Group Policy. Group Policy processes at login, so if the VPN is not connected yet, drive mappings will fail. Many VPN clients support a pre-login or start before logon feature that connects the VPN at the Windows login screen. If that is not available, connect after login and run gpupdate /force to reapply drive mappings.
Why do mapped drives work in the office but not over VPN?
Mapped drives work in the office because your computer is directly connected to the corporate network with access to the internal DNS server and the file server subnet. Over VPN, your computer may not be using the internal DNS server (so server names do not resolve), split tunneling may exclude the file server subnet, or your home network subnet may conflict with the office subnet. The fastest test is to try mapping the drive using the server IP address instead of the server name.
How do I map a network drive using an IP address over VPN?
To map a network drive using an IP address, open File Explorer, click This PC, select Map Network Drive, choose a drive letter, and enter the path using the server IP instead of the name. For example, type \\10.0.1.50\sharename instead of \\fileserver01\sharename. This bypasses DNS resolution entirely and is the quickest workaround when DNS is failing over VPN.
What is split tunneling and does it affect mapped drives?
Split tunneling is a VPN setting that sends only certain traffic through the VPN tunnel while letting other traffic go directly to the internet. It affects mapped drives when the file server subnet is not included in the split tunnel configuration, causing requests to the file server to bypass the VPN entirely. You can check this by running route print in a command prompt and looking for the file server subnet in the routing table.
Conclusion
If you have been wondering why you can’t access a mapped network drive over a VPN, the answer almost always comes down to one of six issues: DNS resolution failures, split tunneling misconfiguration, authentication and login timing, subnet conflicts, Group Policy delays, or Windows 11 TLS compatibility. By running the diagnostic checklist in this guide, you can identify the specific cause in a few minutes and apply the matching fix.
The fastest workaround for most situations is to map the drive using the server’s IP address instead of its name. This bypasses DNS issues entirely and confirms whether the VPN tunnel itself is working. From there, you can work with your IT team to address the root cause permanently, whether that means updating the VPN DNS configuration, adjusting split tunnel routing, or deploying Always-On VPN.
Remote work depends on reliable access to shared files. We hope this guide saves you a support ticket (or ten) and gets you back to work faster. If you are an IT administrator, consider sharing the diagnostic checklist with your remote workers so they can self-diagnose before reaching out.